
Monarx Safety is a PHP malware safety service for serving to hosting suppliers safe buyer’s web sites and functions, significantly towards internet shell assaults. InMotion Internet hosting clients can monitor Monarx exercise at no cost from the cPanel interface.
However what does the Monarx safety service really do? And what are internet shells?
Monarx Safety is simply out there for Shared Internet hosting plans at the moment.
What’s Monarx Safety?
Monarx is a singular sort of next-generation internet firewall (NGFW). It’s targeted extra on the habits of PHP code, not simply the way it seems or it’s signature, each of which might be obfuscated (e.g. polymorphic viruses). This mitigates the potential of recordsdata being falsely marked as malicious, which may result in points in clear web sites, and reduces the period of time required to detect zero-day vulnerabilities.
Right here’s how the precise course of works.
- The Monarx agent is put in on our shared internet hosting servers. The agent consists of two modules. Defend tracks and blocks execution of internet shell payloads. Hunter runs weekly full scans and real-time scans for compromised supply binaries and internet shells.
- The Monarx agent downloads safety guidelines associated to internet apps and content material administration programs (CMS).
- Any recordsdata flagged as malicious by the Monarx agent are robotically processed per safety guidelines and despatched to the Monarx Cloud for additional evaluation, offloading server useful resource calls for.
- PHP-based internet shells/backdoors are blocked from executing, a way they dubbed “post exploit payload prevention.”
- Our system directors are in a position to make use of the Monarx API for higher Safety Data and Occasion Administration (SIEM) throughout all shared internet hosting accounts to raised detect code injection and comparable assaults.
As you’ll be able to see, this software-as-a-service (SaaS) does rather a lot within the background that isn’t widespread with different internet software firewalls (WAF). The most effective half about it: you’ll be able to test Monarx exercise in cPanel however don’t should configure something. Simply know that it’s there.
What’s a Internet Shell?
An internet shell is just a malicious software program used to entry a system remotely with out authorization. Internet shells are a significant menace as a result of they’re laborious to detect whereas permitting hackers admin entry to do no matter they please:
- Web site defacement assaults
- Distributed denial of service (DDoS) assaults
- Privilege escalation to entry restricted providers
- Anything a licensed root person can do
There are three varieties of internet shells.
Bind shell: the sufferer’s system is contaminated to hear on a selected port (a typical backdoor).
Reverse shell (connect-back shell): the system is contaminated to actively search a connection to the cyber attacker’s native machine or command and management (C2) system.
Double reverse shell: a reserve shell the place the goal machine makes use of separate ports for enter and output.
The everyday steps an attacker takes to perform this:
- Exploit a vulnerability to add an internet shell (payload) to a goal machine.
- Transfer the net shell to a extra accessible, public listing.
- Entry the net shell to add or modify recordsdata.
In abstract, stopping internet shell execution reduces the potential of your web site being manipulated for crypto mining, spamming, and different malicious functions.
Methods to Entry Monarx cPanel Plugin
There are not any sophisticated steps required to watch Monarx safety occasions:
- Log into cPanel.
- Below “Security” choose “Monarx Security.”
- Merely refresh (F5) the web page in case you see the next message: “Monarx is still attempting to provision your account. Please refresh the page. If the problem persists, check back later.”
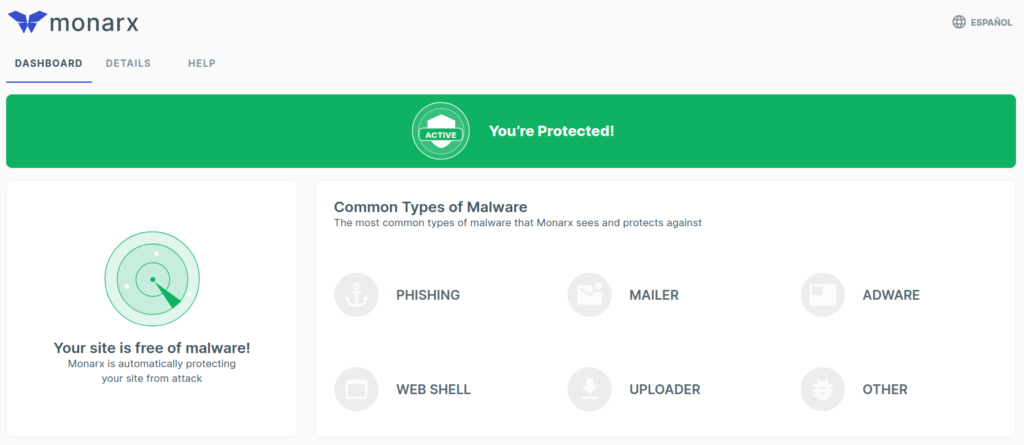
The Monarx dashboard will state that “you’re protected” and “your site is free of malware!” (if not, contact Stay Help). On the precise facet is an inventory of what varieties of malware Monarx fights robotically:
- Uploader entry to your server
- Internet shells which allows superior persistent menace (APT)
- Phishing and cybersquatting websites injected into your server
- Mailer functions for spoofing your electronic mail accounts
- Adware scripts embedded into your website
- Different malware that may infect customers that go to your website
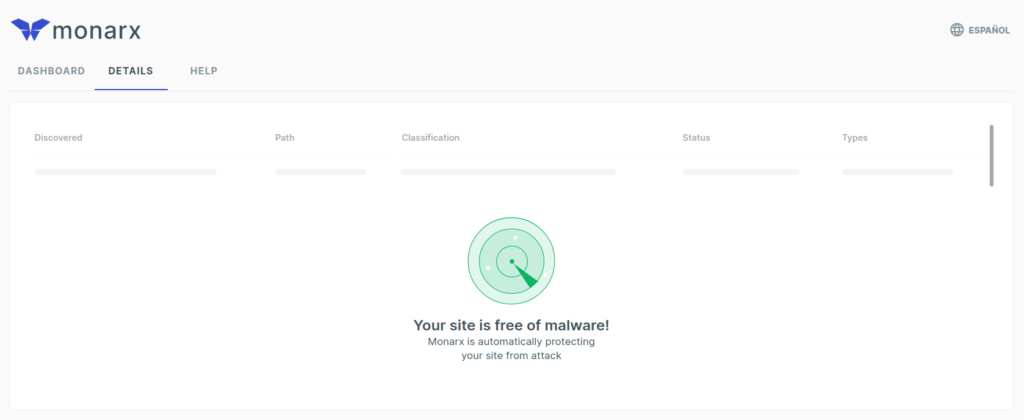
Choose the “Details” tab to view recordsdata in your cPanel server marked as suspicious.
- Date and time found
- Absolute file path
- Classification (malicious or compromised/contaminated)
- Standing of the file (quarantined, blocked from executing, cleaned of malware, or logging for additional motion)
- Sort
There’s one interactive characteristic for finish customers at the moment. If at any level you discover {that a} compromised file was incorrectly marked as clear by Monarx, you’ll be able to submit the file for additional assessment. Merely log into cPanel Terminal, or SSH, and run the next command (changing “filename” with the precise file):
monarx-sample-upload filename
Contact Stay Help for additional help.
Monarx software program captures additional data associated to malware detected for future reference together with:
- File SHA-256 checksum or stronger
- IP tackle and nation of origin
- Affected internet functions (e.g. CMS plugins and themes)
The “Help” part consists of extra data on the Monarx cPanel interface and malware usually.
cPanel Safety
Monarx isn’t a defense-in-depth safety suite. You continue to ought to have a standard firewall, WAF in your internet functions, and antivirus (AV) software program.
Our shared internet hosting plans nonetheless embrace Patchman for monitoring modifications in WordPress, Drupal, and Joomla. Hottest CMSs have safety plugins you’ll be able to set up at no cost.
For those who improve to a VPS or devoted server, you’ll should deal with extra of your safety posture.
- Make sure that an AV scanner (ClamAV or ImunifyAV) is put in and set to robotically scan at the least weekly.
- Harden your conventional firewall. We suggest ConfigServer Safety & Firewall (CSF) or Firewalld.
- Defend your server with a signature-based firewall similar to ModSecurity or Fail2ban.
Tell us you probably have any questions on Monarx safety or internet shell assaults.